Tag Terraform

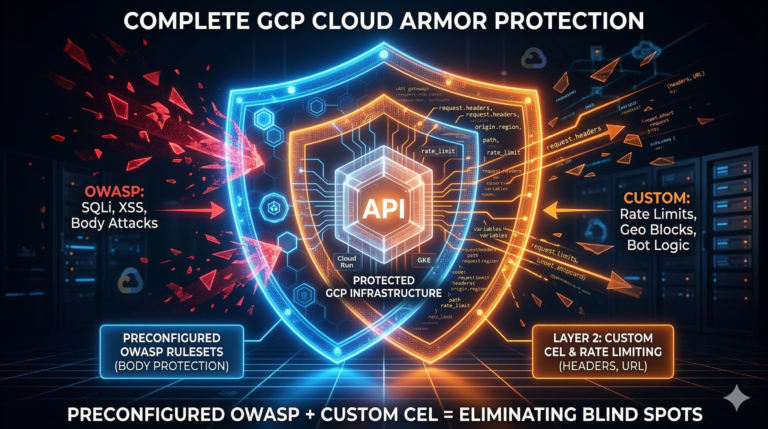
A glowing digital shield divided into two interlocking halves. The left blue half represents preconfigured OWASP body protection, while the right orange half represents custom CEL header and URL validation, illustrating complete Cloud Armor protection.

GCP Cloud Armor: Custom WAF Rules for Enterprise API Protection

Most GCP Cloud Armor deployments follow the same pattern: enable the service, attach the preconfigured OWASP rulesets, move on. It feels complete. The problem is that preconfigured rulesets and custom CEL expressions operate on fundamentally different parts of the request…

A 3D illustration showing the OpenTofu logo on a central processor surrounded by glowing circuit paths and cloud provider icons for AWS Google Cloud and Azure representing modern infrastructure as code.

OpenTofu in 2026: The Greenfield IaC Decision You Need to Get Right

In August 2023, HashiCorp relicensed Terraform under the Business Source License, quietly rewriting the terms that millions of infrastructure teams had built their toolchains on. For organisations already running Terraform in production, the immediate impact was ambiguous enough to justify…

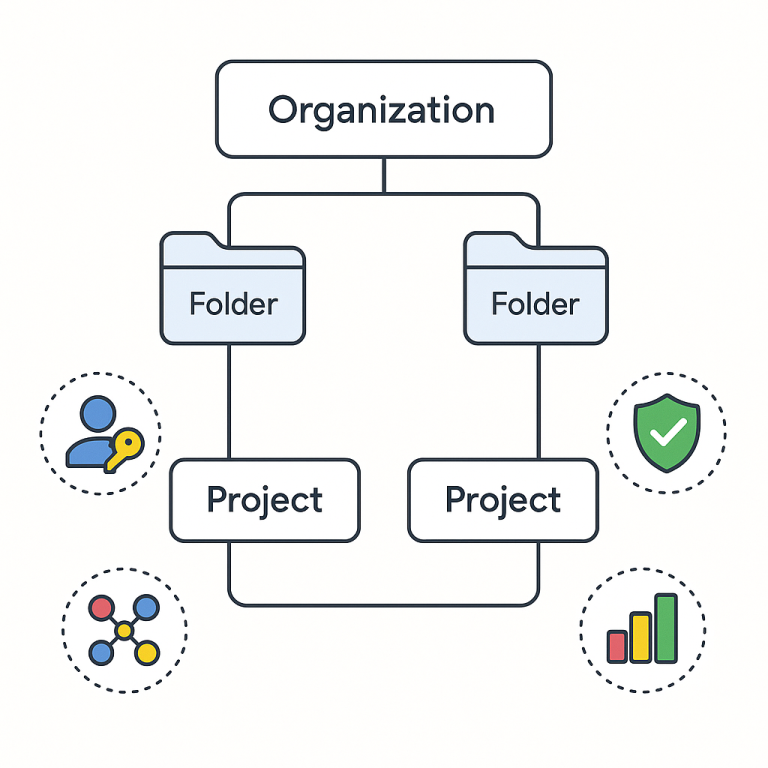
Minimalist GCP landing zone hierarchy showing organisation, folders, projects, and surrounding security, IAM, networking, and monitoring guardrails.”

GCP Landing Zone Setup: A Practical Guide for Cloud Architects

The landscape of Google Cloud Platform adoption shifted dramatically in May 2024. Organisations creating new GCP accounts now receive automatic security baseline enforcement: a paradigm change that elevated landing zones from “nice to have” to foundational infrastructure. For cloud architects…