GCP Artifact Registry Vulnerability Scanning: Block Critical CVEs Before They Reach Production
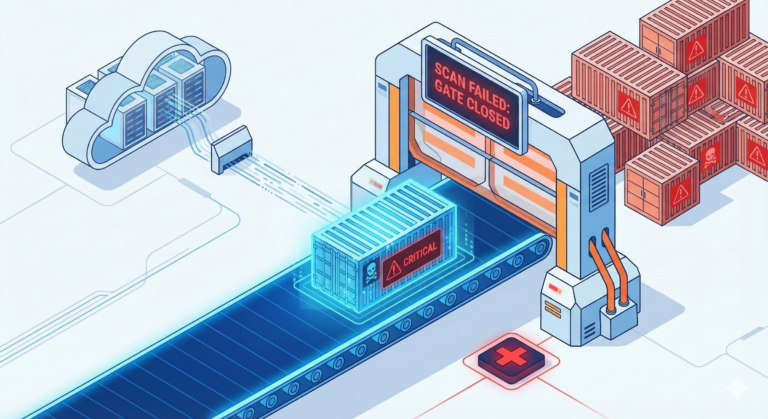
Most GCP teams enable the Container Scanning API, check the Artifact Registry console once, and consider the job done. The scan results sit there, a growing list of CRITICAL and HIGH severity CVEs, while the pipeline keeps pushing images to…